The team at Daphnis Labs redefined what’s possible for Urbanface. They delivered a bespoke, animation-heavy website that remains incredibly quick and functional. The…
Find the failure. Recover a delivery path.
Review the code, infrastructure and release evidence before deciding what to repair or replace.
System review
Code
Data
Cloud
Access
Release
Tools & technologies
- Existing codebase and infrastructure
- Dependency scanners
- Profilers
- Log and trace analysis
- Database diagnostics
- CI/CD checks
Follow the evidence.
Choose a fictional incident and try a contained response.
Sample evidence
Sign-ins fail after a configuration change.
auth / signature mismatch
config / signing key changed
release / previous version available
Working hypothesis
The application instances may be using different signing configurations.
Containment test
Restore a consistent known configuration in the example.
Illustration only; no live system is changed.
Separate recovery from modernisation.
Stabilise
Limit the immediate impact and establish a verifiable recovery point.
Decide
Rank the remaining findings by impact, dependencies and effort.
Modernise
Replace or improve components in agreed stages, with checks between releases.
What you receive.
Findings report
Severity register
Dependency map
Recovery backlog
Verification checks
Handover notes
Revamps and platform migration
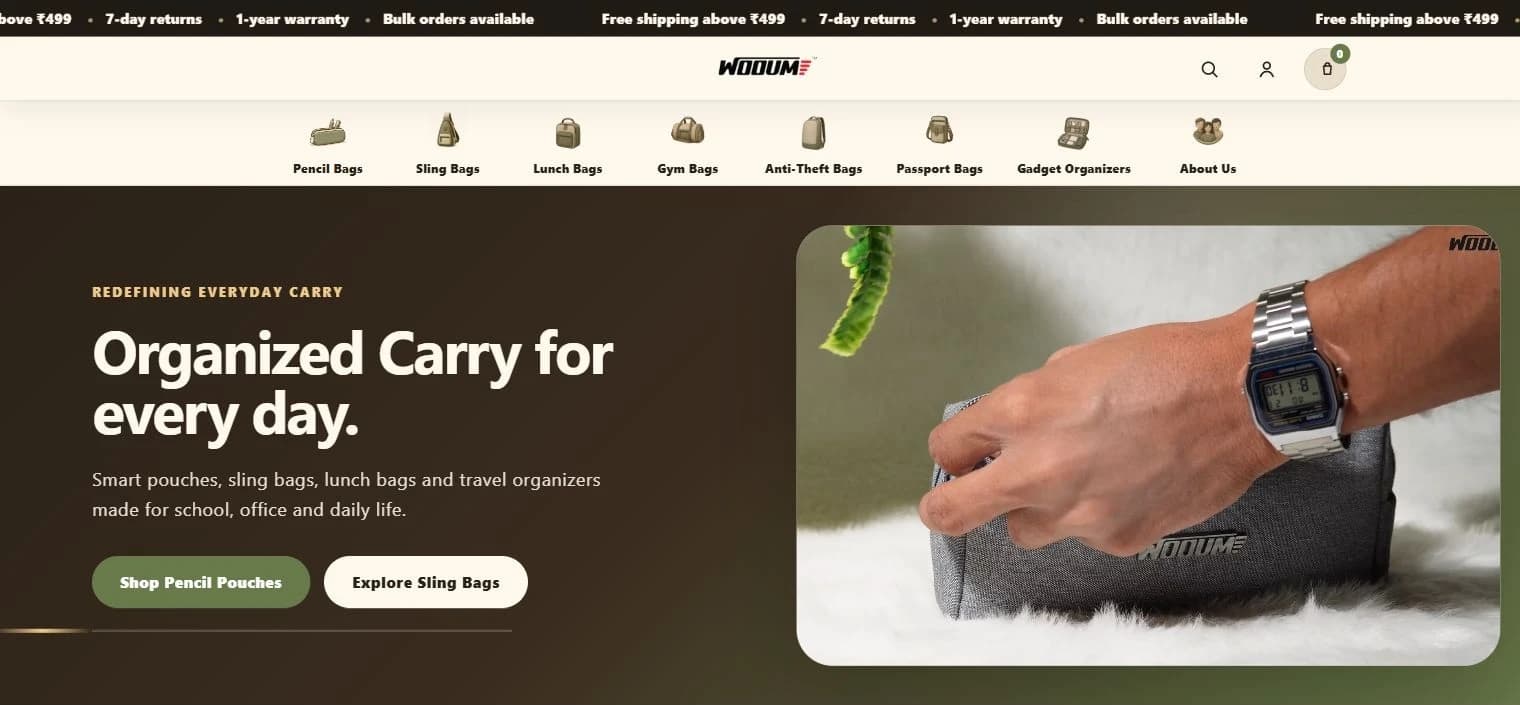
WOOUM
Brand-led design and interactive shopping tools for bags and everyday-carry accessories.
View project
Rimore Store
Shopify improvements connected with search, advertising and social media support.
View project
Yuccabe Italia
A WordPress migration covering the product catalogue, bespoke theme development and warehouse integration.
View project- Founded in
- 2013
- Projects delivered
- 550+
- Client countries
- 43+
- Global offices
- 3
FAQs
What access do you need for an audit?
We agree the minimum access required to inspect repositories, environments, deployment records and relevant logs. Read-only access is used where it is sufficient.
Does an audit include fixing the issues?
Assessment and remediation are separate scopes unless the agreement combines them. Findings identify the evidence, impact and proposed next action before implementation is authorised.
Will you recommend a full rewrite?
Only when the evidence supports it. Targeted repair, staged replacement or retaining the current system may be more appropriate than rebuilding everything.
Can you take over from another supplier?
A transition can cover repository access, infrastructure ownership, dependencies, credentials and operating knowledge. Missing access or documentation is recorded as a constraint.
Is this an emergency response service?
Availability and response expectations must be agreed. This page does not promise an immediate or round-the-clock incident response.
Is this a security certification?
No. The review may identify security-related findings within its agreed scope, but it is not a certification or a substitute for a separately commissioned specialist assessment.
What has stopped working?
Share the symptoms, affected users and the access you can provide. We will define the first review.