Access that holds
Define account boundaries, invitations, session expiry and server-side permission checks.
Build portals and browser-based products where accounts, permissions and daily tasks fit together.
Illustrative access model
Switch between an analyst and a client, then publish the report.
The analyst can see the draft. The client cannot.
Define account boundaries, invitations, session expiry and server-side permission checks.
Agree upload limits, private storage, version history and who can retrieve each document.
Preserve filters, validation feedback and unfinished changes across the agreed browser journeys.
Keep useful foundations. Make the next change at a clear boundary.
We inspect the current sign-in flow, key journeys and data dependencies before choosing an incremental release or a larger replacement.
Need a content-led website?Need delivery across an existing stack?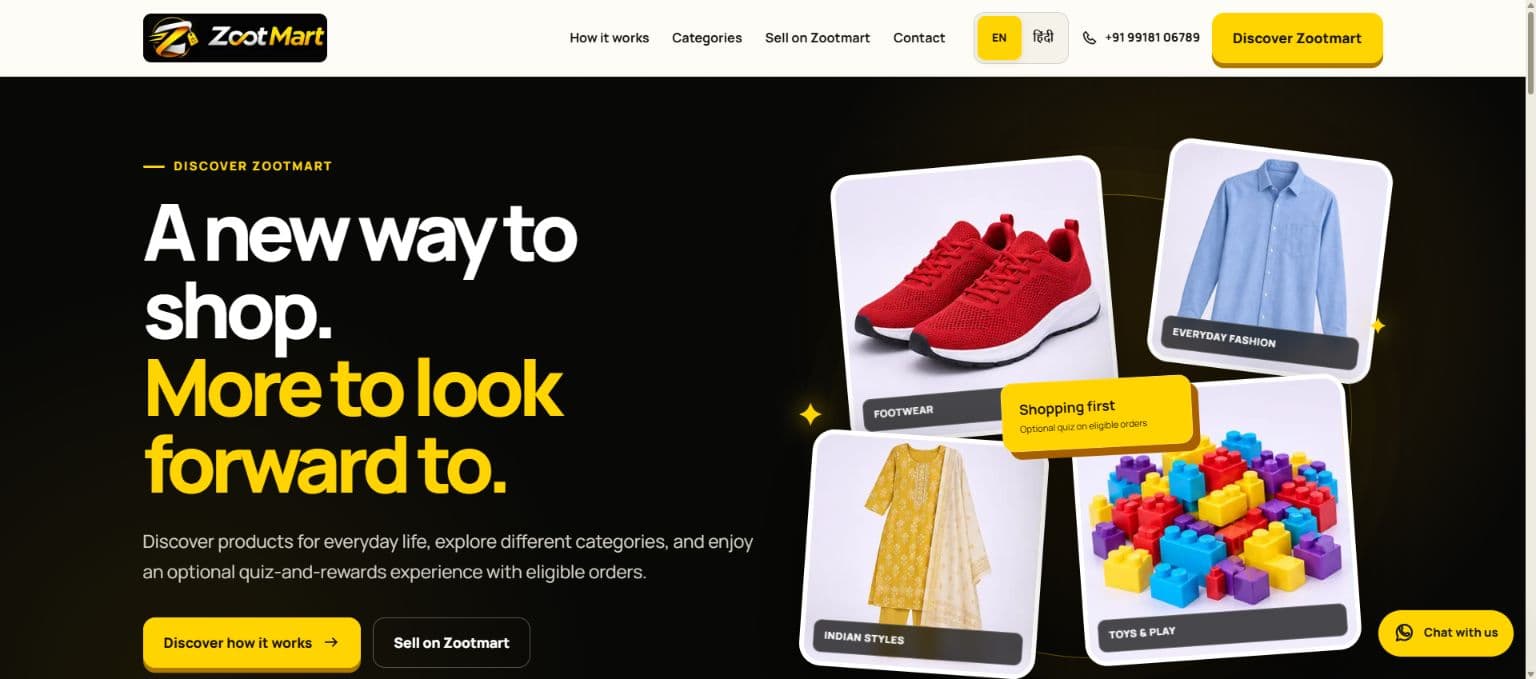
Web, hybrid apps and administration work for a marketplace with a rewards layer.
View project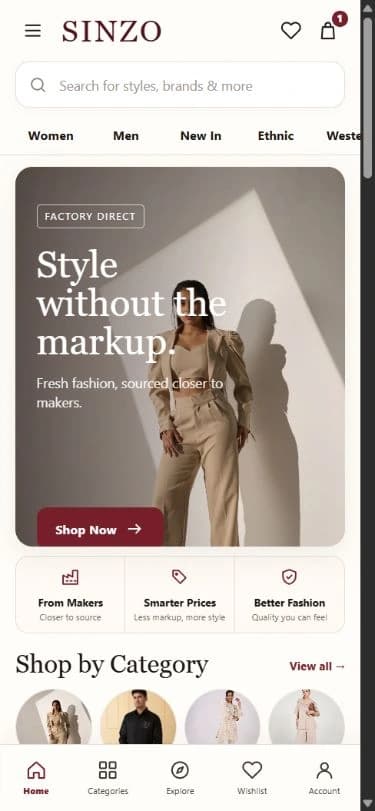
Supplier-data scraping and AI engineering for a cross-border shopping and warehouse platform.
View project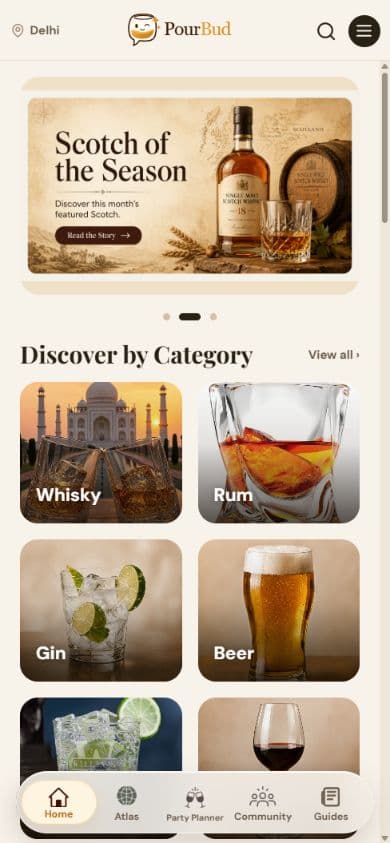
A complete consumer platform connecting city-wise drink data with AI, regional stories and community.
View project
A shared-hosting application with encrypted document storage and a staff review console.
View projectA web application lets signed-in users work with records and complete tasks. A content-led website primarily helps visitors find information and take a next step. Some products need both.
Yes. We review its interfaces, authentication, data model and deployment before agreeing which areas to extend or replace.
Yes, when tenant isolation is part of the scope. Access boundaries need server-side enforcement and tests; hiding a screen alone is not a security control.
The agreed journeys are designed and tested for mobile browsers. Offline operation, device integrations or app-store distribution need a separate scope decision.
Bring the user roles, a recurring task and the systems it touches.
What our clients value about working with Daphnis Labs.
The team at Daphnis Labs redefined what’s possible for Urbanface. They delivered a bespoke, animation-heavy website that remains incredibly quick and functional. The…
We wanted a unique, 'one-of-a-kind' feel for Glareen, and Daphnis Labs delivered an ecosystem that is both beautiful and technically superior. Their expertise in…
The level of technical depth Daphnis Labs brought to our Game project is unparalleled. While the front-end reel games are visually stunning and highly engaging, the…
Practical perspectives on AI, product engineering, commerce and modern software delivery.
Measure recovery by restoring into an isolated environment and checking the application, roles and dependencies that need the data.
Read Blog
Classify responses before caching them, make cache keys reflect their audience and test what happens when permissions change.
Read Blog
Review database roles, background jobs and exports together when designing row-level security for a shared application database.
Read Blog
Plan rollout, fallback behaviour and flag removal together so temporary release controls do not become permanent product complexity.
Read Blog
Connect traces, metrics and structured logs around a real failure path so the team can locate an incident and choose a next action.
Read Blog
Define permissions around concrete actions, and make an approval apply to the exact message or record that will be changed.
Read Blog
Separate parsing, validation and approval so an ordinary spreadsheet upload does not become an opaque bulk edit.
Read Blog
Give images, third-party scripts and interactions measurable limits, then investigate regressions by page template and device.
Read Blog
Help people complete a form with persistent labels, specific errors, preserved answers and a clear confirmation state.
Read Blog
Separate event receipt from order processing, record duplicate deliveries and recover work that stops halfway through.
Read Blog