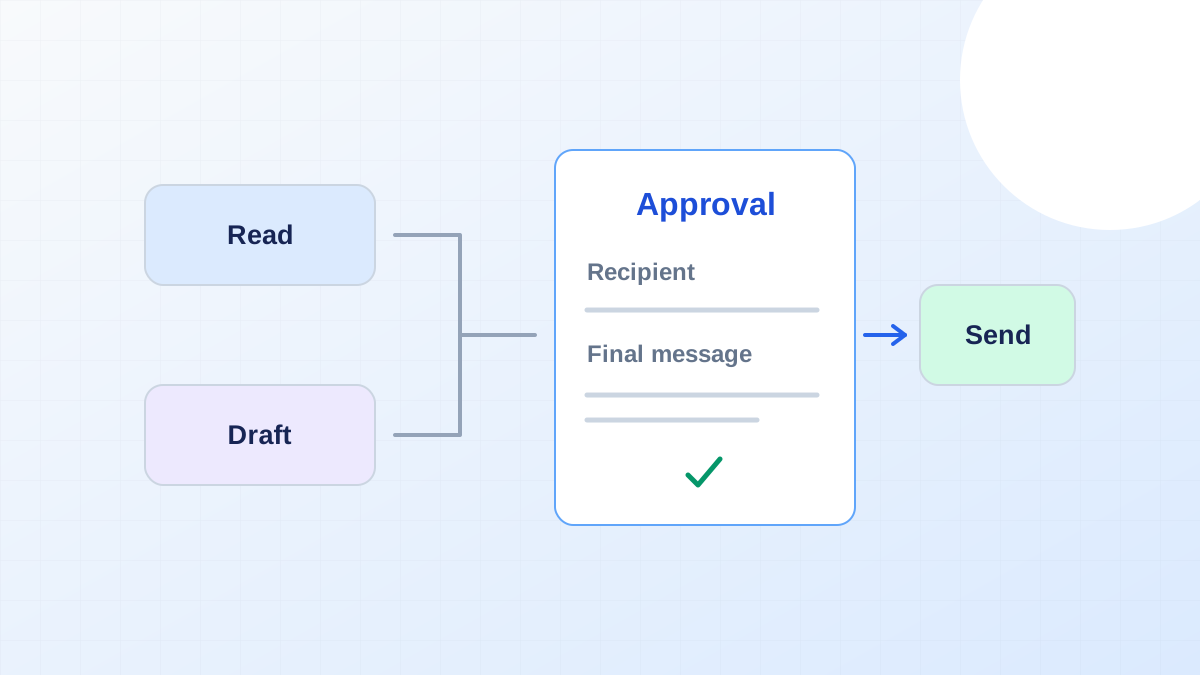
An assistant that can read a customer record does not automatically need permission to change it or send a message. Combining these actions inside one broad tool makes it harder to explain what the assistant is allowed to do. Separate capabilities around the business action and the consequence of getting it wrong.
Describe capabilities in verbs
Start with actions such as search tickets, read an assigned account, draft a reply and send an approved reply. Specify the resource scope for each action. Read-only access can still expose information, so limit it to the records the current user is entitled to view. Keep credentials in the execution layer rather than placing them in prompts or tool descriptions.
The OWASP authorization guidance recommends least privilege and permission checks on every request. Apply those checks in the service that executes the tool. A prompt telling the assistant to behave carefully is not a substitute for a server rejecting an unauthorised action.
Bind approval to the final payload
For a send action, show the recipient, subject, message and attachments together. Bind the approval to that exact payload and the acting identity. If the assistant changes the recipient or text afterward, require a new approval. Avoid a reusable yes token that can authorise a different action later in the conversation.
Keep drafting useful even when sending is unavailable. A support worker should be able to edit or discard a proposed reply. When execution fails, report whether anything was sent before offering a retry. An ambiguous network result needs reconciliation, particularly where the receiving API does not support idempotent requests.
Test the boundary directly
Attempt a tool call for an unassigned account, alter a payload after approval and replay an expired approval. The execution service should reject each attempt regardless of what the model says. Record the decision, actor and affected resource without copying unnecessary customer information into logs.
Use this action map when scoping agentic automation or an MCP server. For assistants that also retrieve documents, connect it to the separate RAG permission model so search access and action access do not drift apart.